
V-Core · Identity
Identity & Access
Management
Watch a sign-in flow through one secure path: verified, challenged with MFA, single-signed-on, launched into the right apps and granted least-privilege access, each step scored and audited.
A demonstration of one sign-in: verified, MFA-challenged, single-signed-on, then launched into the right apps with least-privilege access, each step recorded.
See the real product
The Identity
console.
The environment your administrators use to run identity, access and security. Captured 2026-08. Click to inspect it full-size.
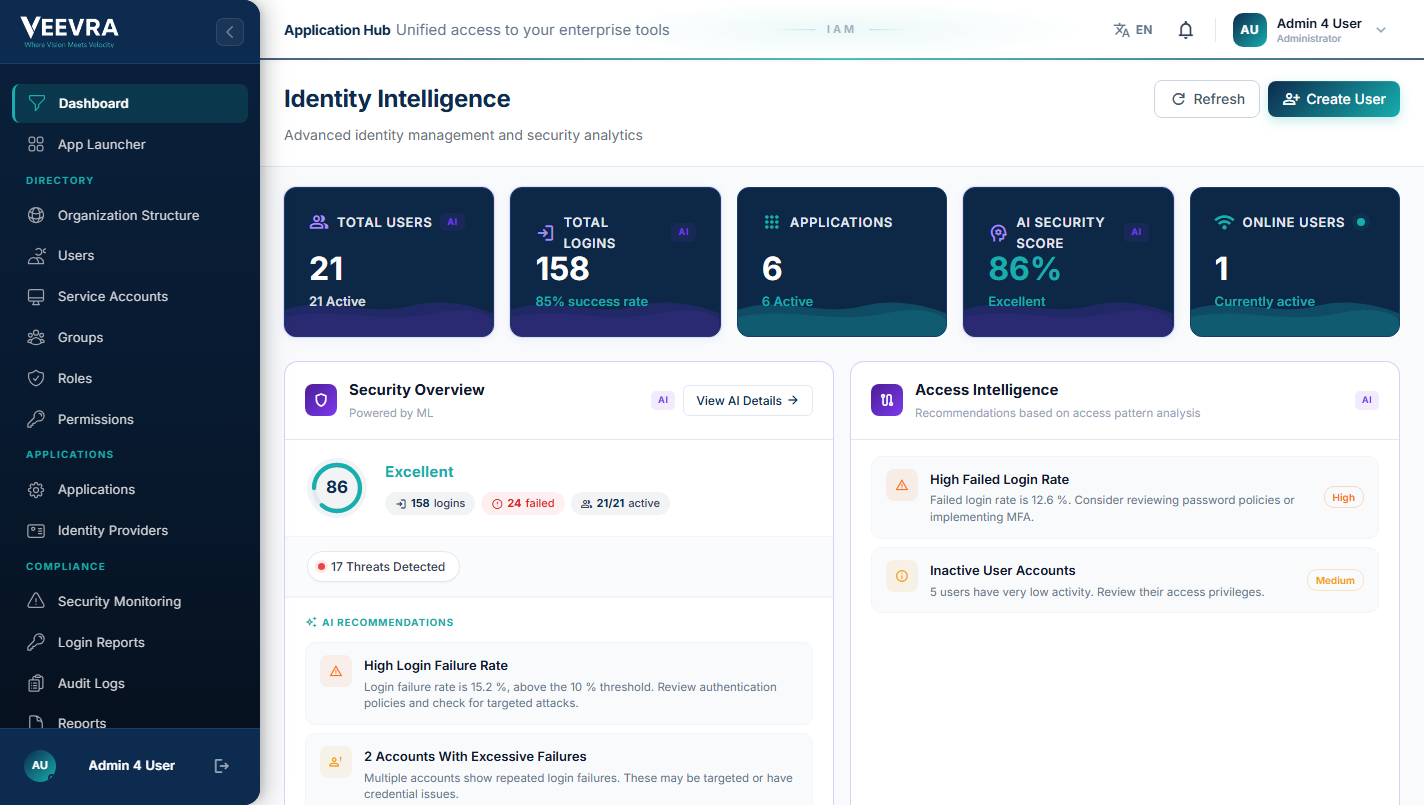 Security analytics
AI risk scoring
Users & activity
Inside Identity
Manage access with
intelligence built in.
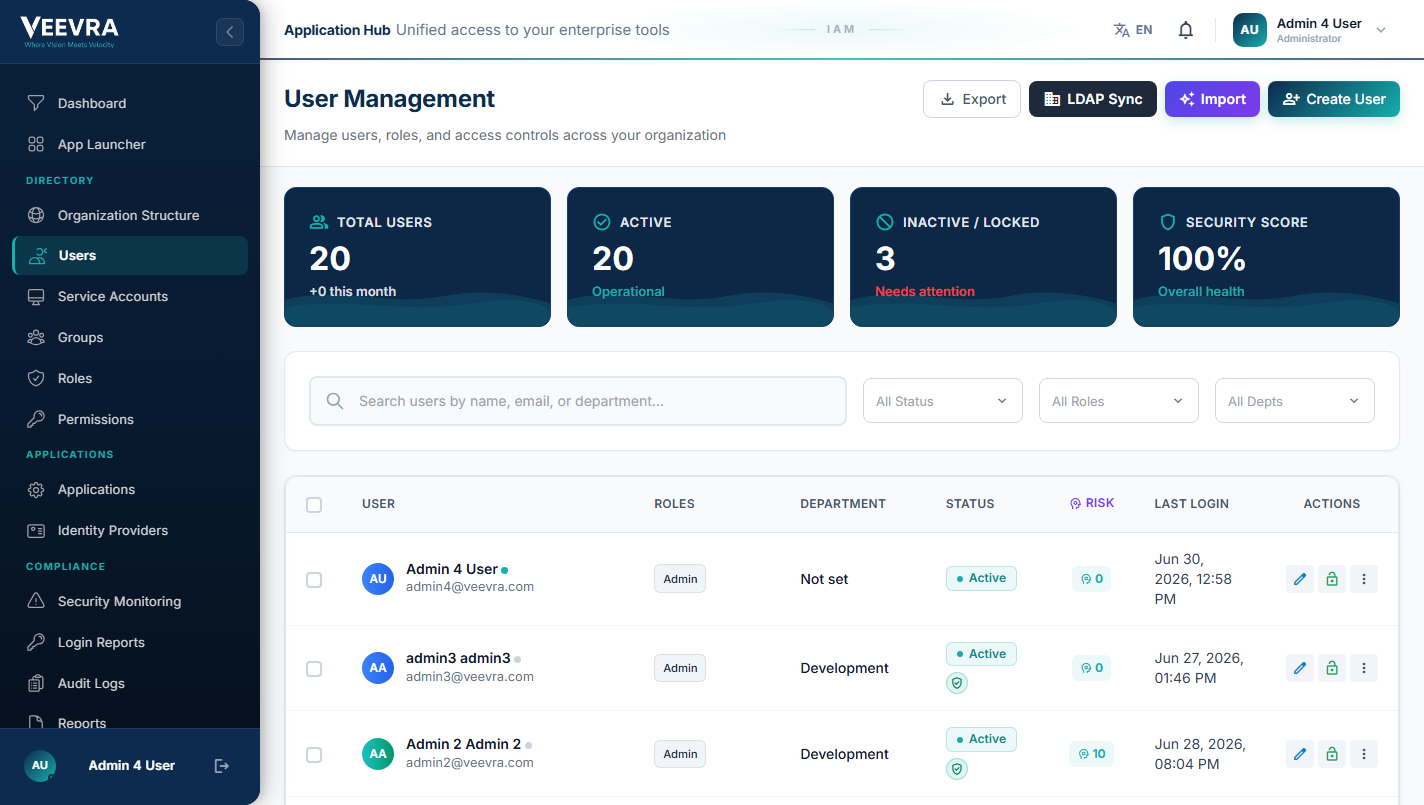
Every user, scored for risk
Provision from your directory, import and export in bulk, and see each user’s roles, department and a live AI risk score. The organization carries a single security score you can act on.
- Directory sync
- AI Risk Score
- Bulk Import
- Security Score
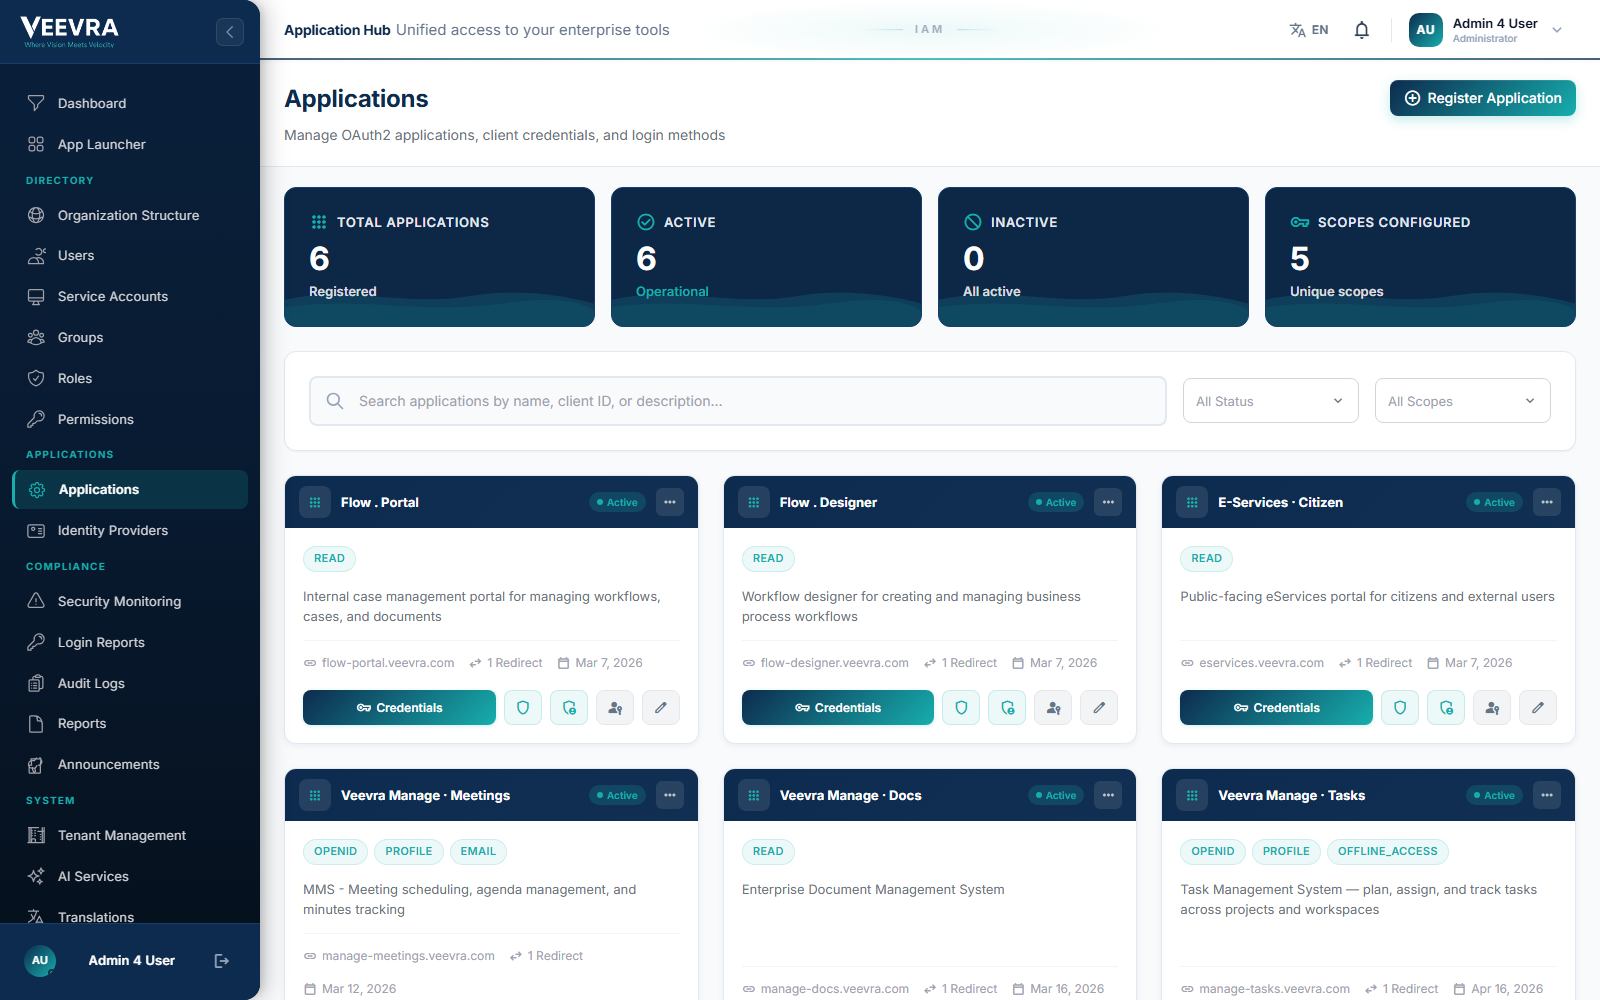
One sign-on for every app
Register OAuth2 applications with client credentials and scoped permissions, then give users single sign-on across all of them. Veevra’s own products and your apps live in one hub.
- OAuth2 / OIDC
- Client credentials
- Scoped permissions
- Login methods
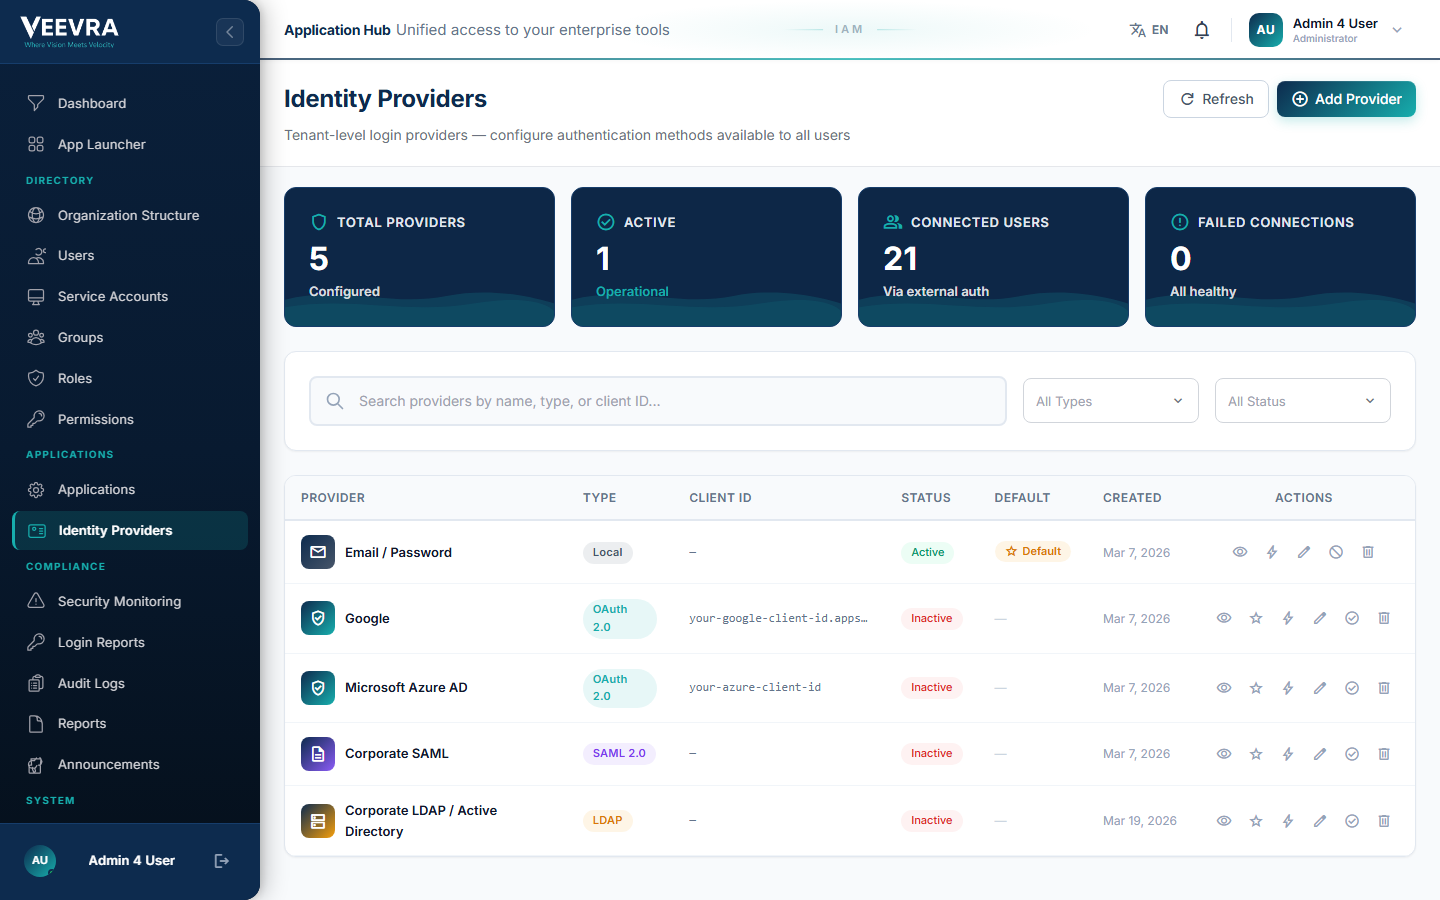
Least-privilege access, by design
Define roles with granular permissions across resources and applications. Assign them to users and groups so everyone gets exactly the access they need, and nothing more.
- RBAC / ABAC
- Granular permissions
- Groups
- Resource scoping
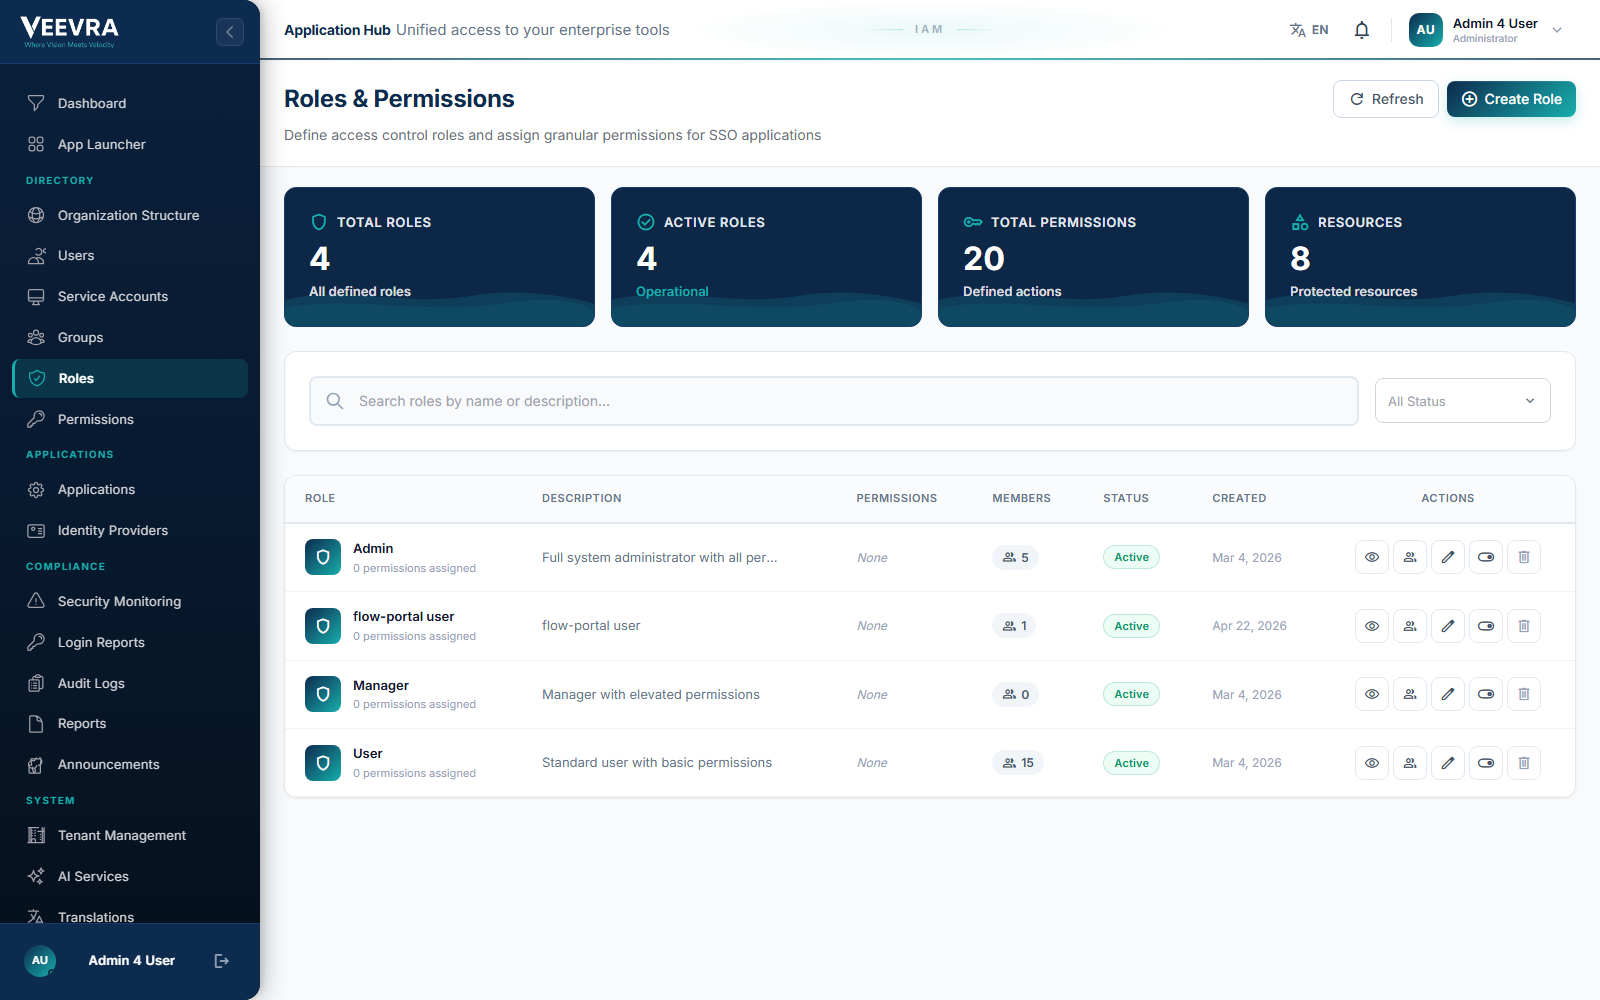
Every action, on the record
A complete audit trail of who did what, where and when: timestamp, user, action, resource, IP, category and status. Login reports and security monitoring sit alongside it.
- Audit Logs
- Login Reports
- IP & device
- Security Monitoring
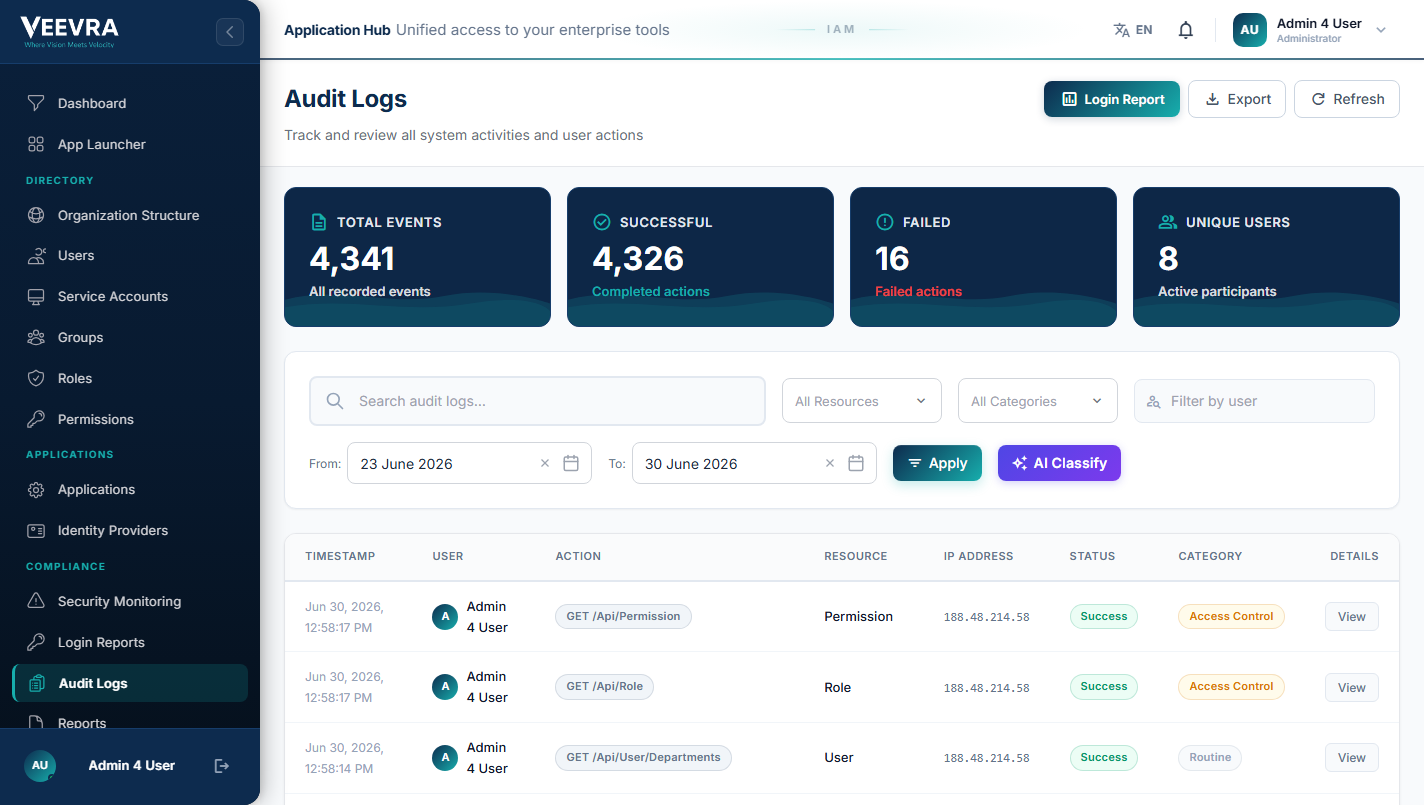
AI security, governed centrally
Identity can connect to AICP through a registry of AI services — the optional governed AI that provides risk scores, an ML security overview and anomaly detection, the same governed AI available across the platform.
- AI Services registry
- Risk scoring
- Anomaly detection
- ML security score
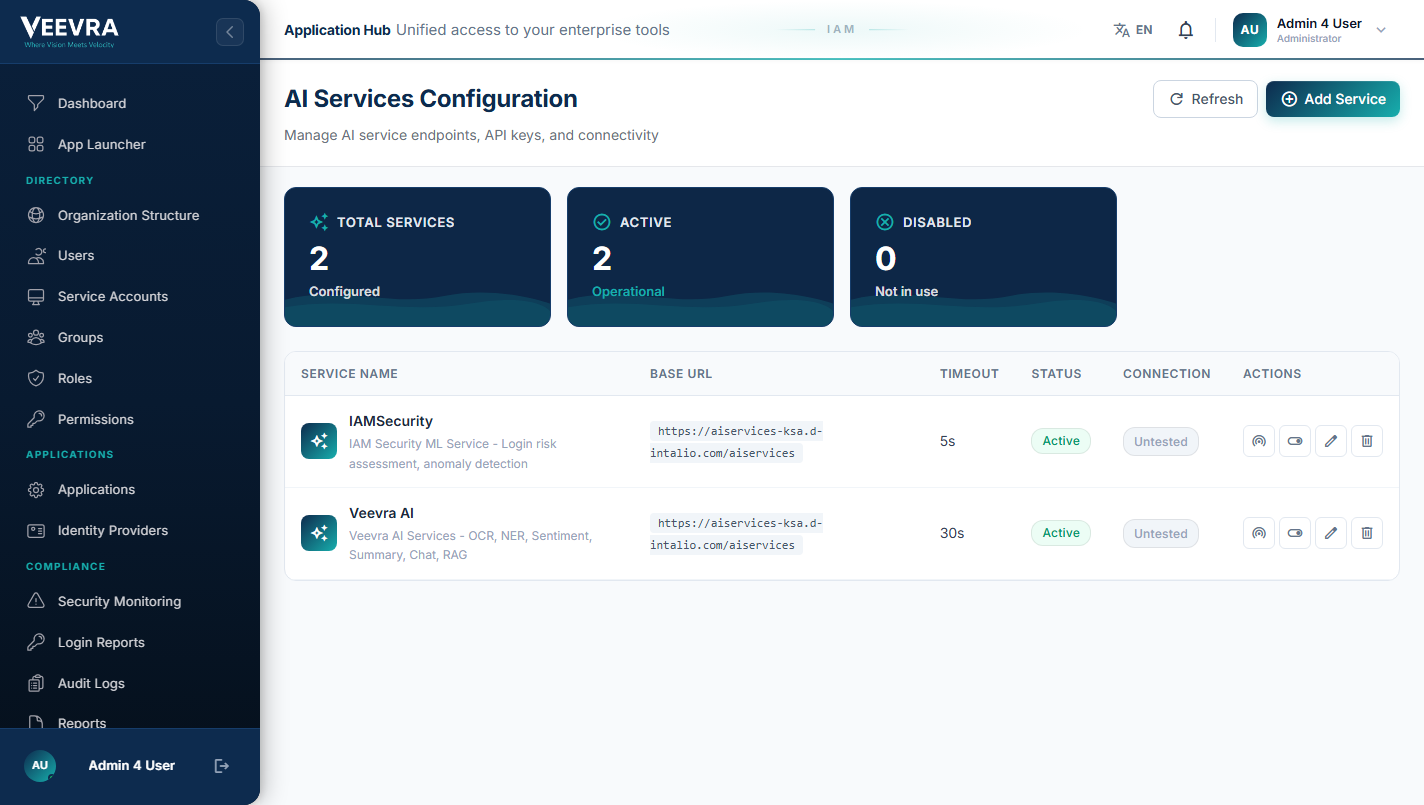
One login,
every provider
Configure the authentication methods available to everyone: local accounts, Google and Microsoft Azure AD (OAuth 2.0), corporate SAML and directory services, each with per-provider status, alongside a connected-users total.
- OAuth 2.0
- SAML 2.0
- Directory
- Per-provider status
Capabilities
Intelligent access management.
Context-aware identity controls that adapt to risk, enforce policy and protect every access point.
Single Sign-On
One identity, every application. Context-aware session management across OAuth 2.0, OpenID Connect and SAML 2.0, with real-time access revocation.
Adaptive Multi-Factor Auth
Behavior-based MFA that adjusts to risk level, device trust and location. Supports TOTP, WebAuthn/FIDO2 and biometric, without slowing users down.
Dynamic Access Control
Centralized policy enforcement with granular roles, groups and permission inheritance. Define and enforce who accesses what, across every system.
Directory Integration
Directory sync with automated provisioning. Users, groups and org structures stay current, with zero manual effort.
Unified App Launcher
Personalized, role-based application dashboard. Users see only what they're authorized to access. That shrinks the attack surface and support requests alike.
Multi-Tenant Isolation
Fully isolated tenant environments with independent policies and configurations. Built for SaaS, shared infrastructure and multi-entity deployments.
Security
Proactive threat detection.
Continuous behavioral analysis scores sign-ins and flags indicators of compromised credentials, insider threats and anomalies for your security team to act on.
Anomaly Detection
Detect compromised credentials and insider threats before they become security incidents.
Threat Classification
Automatically classify and prioritize threats, so analysts spend their time on the ones that matter.
Behavioral Analytics
Reduce false positives with behavioral pattern analysis that learns your organization's norms.
Real-Time Risk Scoring
Every authentication event receives an instant risk score, triggering adaptive responses automatically.
Architecture
How it fits the platform.
Identity is a capability of the V-Core family. It works independently and can be purchased individually or as part of the complete V-Core family.
What it is
Identity, access, security and audit API-first and multi-tenant.
Part of V-Core
This is a capability of the V-Core family, available on its own or as part of V-Core.
Optional AI enhancement
This capability works without AI. Customer-controlled deployments may be enhanced through separately deployed AICP. Veevra-hosted SaaS may be enhanced through a separate AICP Enterprise subscription.
Deploy your way
Deploy on-premises, air-gapped, in your public or private cloud, as Veevra-hosted SaaS, or through a hybrid model.
Where it's used
Trusted access, across sectors.
See it on your systems
Get a tailored walkthrough
Leave your details and our team will show you Veevra working in your environment, with no commitment.